SAN ANTONIO, October 21, 2026 — Defense Unicorns has launched an end-to-end Cybersecurity Maturity Model Certification solution designed to help contractors across the Defense Industrial Base accelerate certification and preserve contract eligibility. The move arrives as the Pentagon finalizes rulemaking that will tie federal contract awards directly to verified cybersecurity maturity.
The Framework Takes Shape
The Cybersecurity Maturity Model Certification is an assessment framework built atop standards published by the National Institute of Standards and Technology. It was developed by the Office of the Under Secretary of Defense for Acquisition and Sustainment through contracts with Carnegie Mellon University, the Johns Hopkins University Applied Physics Laboratory, and Futures Inc. The program, now overseen by the DOD CIO office, exists to verify that contractor information systems processing, transmitting, or storing sensitive data comply with mandatory security requirements.
CMMC organizes practices into domains mapping directly to NIST Special Publication 800-171 and NIST SP 800-172 families across three levels. Level 2 requires implementation of the 110 security requirements in NIST SP 800-171 Revision 2 for protecting Controlled Unclassified Information. The framework will not be enforced on federal contracts until final rulemaking is completed and incorporated into the 32 and 48 Code of Federal Regulations.
From FISMA to Flow-Down
The current mandate has roots in the 2002 Federal Information Security Management Act, which required every federal agency to develop, document, and implement an agency-wide information security program. The same year, the Cybersecurity Research and Development Act authorized appropriations to the National Science Foundation and NIST to establish new computer and network security research programs. Those legislative pillars fed the development of the security requirements now codified in CMMC.
For years, contractors self-attested to NIST 800-171 compliance. The shift to third-party verification changes the technical reality. An authorized CMMC Third-Party Assessment Organization (C3PAO) must now validate the controls. Tagup, a defense technology company founded at MIT, recently achieved Level 2 following an independent assessment by Sera Brynn, a certified C3PAO. The assessment evaluated safeguards including access controls, incident response, personnel security, and system monitoring.
The Burden on Smaller Shops
Department of War contract eligibility is now tied directly to cybersecurity readiness. Contractors face pressure to navigate complex technical controls, gap remediation, and extensive documentation requirements. Defense Unicorns argues that small businesses, independent software vendors, and enterprise contractors alike risk losing eligibility if they cannot produce assessor-ready evidence packets containing tailored System Security Plans, policies, procedures, architecture diagrams, and supporting databases.
The company’s solution targets four pain points: end-to-end implementation and maintenance of security controls, vendor-agnostic integration within existing IT environments such as Microsoft 365 and Google Workspace, generation of audit-ready compliance packages, and collaboration with C3PAOs to remediate failed assessments. The pitch is that contractors should not have to overhaul existing infrastructure to satisfy the flow-down requirements.
Consolidation Pressure
As ever, the detail that matters is the cost of continuous compliance. Year-round maintenance of evidence, scope changes, and evolving flow-down requirements favor organizations with dedicated compliance teams. Smaller contractors must either absorb the overhead, partner with managed service providers, or exit the market. The emergence of turnkey solutions like Defense Unicorns CMMC signals a maturing ecosystem where certification becomes a service layer rather than an internal capability.
Jon Garrity, CEO of Tagup, framed the certification as a customer requirement: commanders make sustainment decisions using their Manifest platform, and protecting the information behind those decisions is the contractor’s responsibility. Independent verification lets customers focus on readiness rather than auditing their vendors’ cyber hygiene.
What Eligibility Means Now
The Defense Industrial Base is entering a period where contract eligibility is binary: certified or not. Upcoming guidance from the CMMC office is expected to help companies determine what level of accreditation they should seek depending on their role as a prime or subcontractor. Until final rulemaking hits the CFR, the timeline remains fluid, but the direction is fixed. The technical reality under the hood is NIST 800-171 Rev 2 controls, assessed by a C3PAO, maintained continuously. Contractors who cannot demonstrate that posture will find themselves outside the gate.
Accreditation Body Oversight
While the Department of Defense CIO office currently oversees the CMMC program, the accreditation of the assessment framework itself is managed by a distinct entity. The Cybersecurity Maturity Model Certification Accreditation Body oversees the program under a no-cost contract. This structural separation ensures that the validation of the framework and the certification of assessors operate under specific contractual and administrative guidelines distinct from broader DOD IT governance.
The framework’s design explicitly targets the protection of two specific data categories: Controlled Unclassified Information (CUI) and Federal Contract Information (FCI). The primary goal is to ensure appropriate protection for these data types when they are stored and processed by partners or vendors. By verifying that information systems used by contractors to process, transmit, or store sensitive data comply with mandatory security requirements, the program aims to increase trust in measures of compliance across the Defense Industrial Base.
This verification process extends to the specific NIST standards referenced in the model. The framework provides a model for contractors to meet security requirements from NIST SP 800-171 Revision 3, titled “Protecting Controlled Unclassified Information in Nonfederal Systems and Organizations.” Additionally, some contracts will include a subset of requirements from NIST SP 800-172, which serves as an enhanced security supplement to SP 800-171. These standards form the technical backbone of the domains that map directly to the CMMC levels.
Sources
- Defense Unicorns Launches End-to-End CMMC Solution to Help Defense Contractors Accelerate Certification and Preserve Contract Eligibility
- Cybersecurity Maturity Model Certification
- Tagup Achieves Cybersecurity Maturity Model Certification (CMMC) Level 2
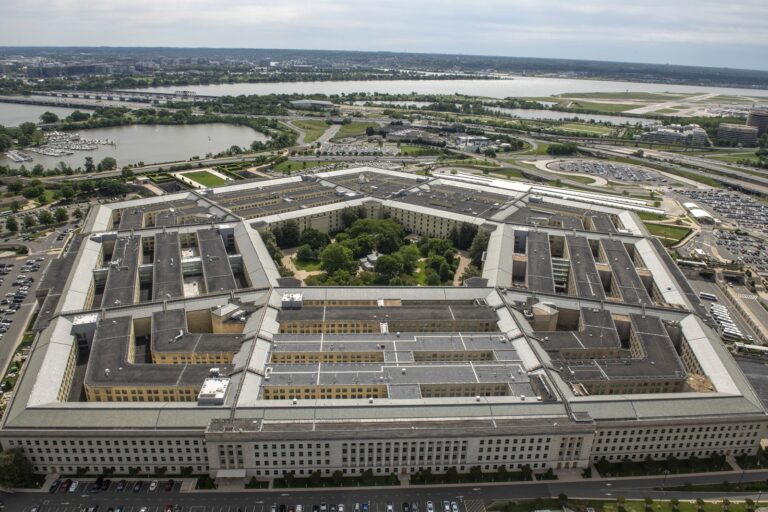
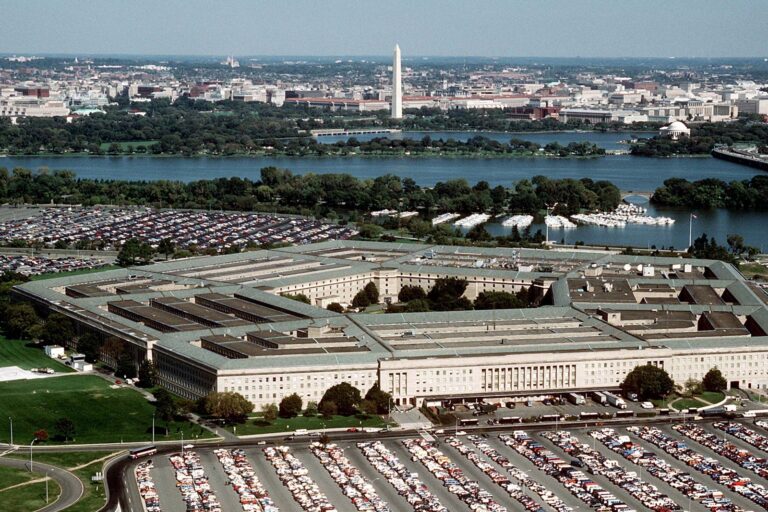
Photo: "DoD photo by Master Sgt. Ken Hammond, U.S. Air Force." (Public domain)